
AI becomes risky when it stops being a blank chat box and starts touching real business systems
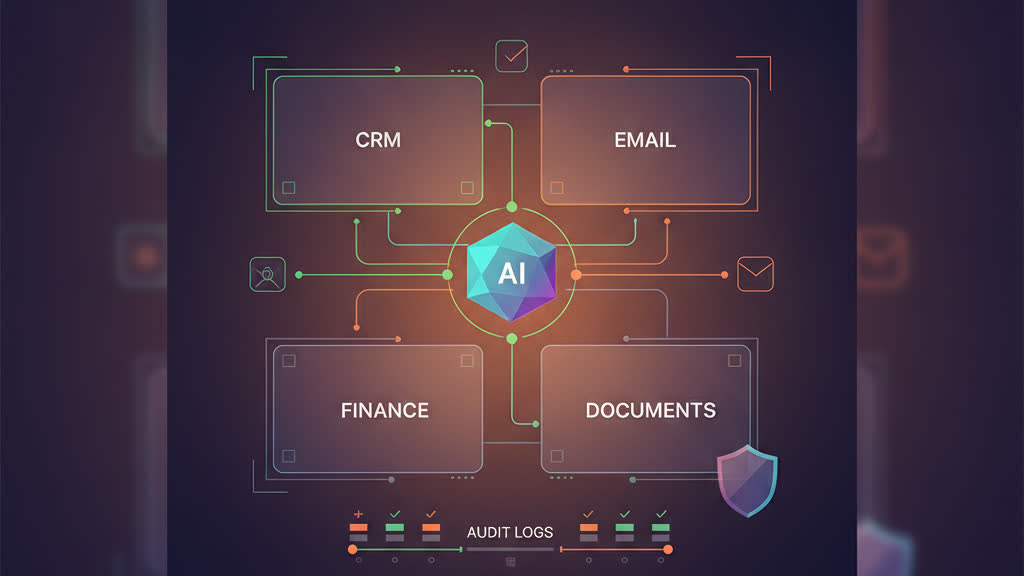
AI becomes risky when it stops being a blank chat box and starts touching real business systems. A chatbot used for rewriting a public brochure is low risk. An assistant that can search the company drive, read CRM notes, summarise customer emails, inspect finance records or draft replies from a shared inbox is a different thing altogether.
The danger is not only that sensitive data might be stored by a vendor. That matters, but it is not the whole story. The practical danger is that AI can combine information from many places, make private inferences, expose material to the wrong person, follow malicious instructions hidden in a document, or act with permissions that were granted too casually.
GOV.UK's Cyber Security Breaches Survey 2025 found that 43% of UK businesses reported a cyber breach or attack in the previous 12 months. That is about 612,000 businesses. The same survey found phishing remained the most common breach type, affecting 85% of businesses that identified a breach or attack. AI does not remove those old risks. It can make them faster, more convincing and harder to notice.
For a UK SME, the sensible starting point is to treat AI access like a privileged user account. Ask what the AI can read, what it can write, what it can remember, what humans can review, where logs are kept, who the supplier uses underneath, and how you turn it off. If those answers are unclear, the system is not ready for sensitive business data.
The first risk is data leakage
The first risk is data leakage. Staff may paste client data, employee data, contract terms, board notes or commercial plans into a tool that is not approved for that data. Even when enterprise settings prevent model training, prompts and outputs may still be logged, retained, reviewed for abuse monitoring, or processed by subprocessors. You need the facts, not reassurance.
The second risk is over-permissioned access. Many AI tools become useful by connecting to Microsoft 365, Google Workspace, Slack, HubSpot, Salesforce, Xero, SharePoint, Dropbox, Zendesk or other systems. If the permissions are too broad, the AI may retrieve confidential files, historic complaints, HR notes or director emails for someone who should never see them.
The third risk is prompt injection. A malicious instruction can be hidden inside a web page, email, PDF, ticket or document. The AI may treat that instruction as part of the task and ignore the business rules you thought were controlling it. This matters most when the AI can browse, retrieve documents, call tools or take action.
The fourth risk is inference. AI can reveal sensitive information without copying the original file. It might infer that a customer is in financial difficulty from payment notes, that an employee has a health issue from HR records, or that a deal is likely to fail from internal emails. Privacy risk is not limited to raw data disclosure.
The fifth risk is weak supplier control. Your AI provider may rely on model vendors, cloud platforms, analytics providers, support tools and human reviewers. If you do not know the subprocessor chain, data locations, retention terms, incident process and training policy, you do not know where the risk sits.
The sixth risk is poor logging. If nobody can see which user asked the AI what, which sources were retrieved, what answer was given and whether any action was taken, you cannot investigate complaints, data breaches, wrong outputs or insider misuse properly.
The seventh risk is automation without human ownership. Once an AI can send emails, update records, create invoices, approve exceptions or trigger workflows, a privacy mistake becomes an operational incident. Human review is not bureaucracy. It is the control that stops a bad answer becoming a business action.
If the AI processes personal data
If the AI processes personal data, UK GDPR applies. That includes customer records, staff data, prospect lists, call transcripts, support tickets, CVs, email content, finance notes, photos, identification documents and behavioural data. It can also include inferences the AI creates about a person.
The ICO's guidance on AI and data protection is clear that AI raises accountability, transparency, lawfulness, accuracy, fairness, security, data minimisation and individual rights issues. In plain English, you need to know why you are using AI, what data goes in, where it goes, how long it is kept, who can access it, how people are told, how outputs are checked and how rights requests will be handled.
A data protection impact assessment is usually needed when AI is connected to meaningful personal data, especially if the tool profiles people, supports decisions, handles special category data, monitors staff, assesses customers, or creates outputs that affect access to a service. A simple internal writing tool may not need a heavy process. An AI assistant reading customer files almost certainly deserves one.
The right question is not whether AI is allowed under UK GDPR. It is allowed if you can comply. The right question is whether this specific tool, supplier, workflow, permission model and data set can be justified, documented and controlled.
Before connecting AI to business data
Before connecting AI to business data, ask direct questions and insist on written answers. The first group is about data use. Will prompts, files, retrieved snippets or outputs be used to train or improve models? Are they retained? For how long? Can you configure retention? Can humans review them? Can you delete them? Can you export logs?
The second group is about location and supply chain. Where is data processed and stored? Which subprocessors are involved? Does the supplier use OpenAI, Anthropic, Google, Microsoft, AWS, Azure, a private model, or a brokered model layer? Can that change without notice? Are international transfers covered properly?
The third group is about permissions. Which systems can the AI access? Does it inherit user permissions or use a shared service account? Can access be limited by folder, mailbox, object, customer type, department or role? Can it write as well as read? Can it send messages externally? Can admins see every connected app and revoke access quickly?
The fourth group is about security operations. Is there multi-factor authentication for admin users? Are logs available? Is there an incident notification commitment? Does the supplier provide penetration testing summaries, ISO 27001, SOC 2 or Cyber Essentials evidence? None of those badges proves safety on its own, but weak evidence tells you something.
The fifth group is about change. AI tools change quickly. Ask how model updates, new connectors, new memory features, new agent capabilities and data processing changes are communicated. GOV.UK's AI Cyber Security Code of Practice says AI has distinct risks including data poisoning, model obfuscation, indirect prompt injection and operational differences around data management. That is exactly why supplier change control matters.
A safe first implementation is narrow
A safe first implementation is narrow. Pick one workflow, one data source, one owner and one success measure. For example, let AI summarise support tickets for internal review, but do not let it send customer replies. Let it search a curated policy folder, but do not give it the whole company drive. Let it draft CRM notes, but require a human to approve them before saving.
Classify your data before connecting it. A practical SME model is public, internal, confidential, personal data and restricted. Public data can be used freely. Internal data needs staff-only controls. Confidential data needs tighter permissions. Personal data needs UK GDPR checks. Restricted data, such as special category data, legal matters, acquisition plans, payroll, safeguarding issues or board papers, should be excluded unless there is a strong reason and a stronger control set.
Set the AI up with least privilege. That means the smallest access needed to do the task. Do not connect the managing director's mailbox because it is convenient. Do not connect all SharePoint sites because folder permissions are messy. Fix the permissions first. AI is very good at finding the sensitive document you forgot existed.
Log the system from day one. You need user, time, prompt, data source, retrieved documents, output and action taken. For higher risk workflows, keep a review sample. In the first 30 days, review failures weekly. After that, review monthly unless the system touches sensitive data or customer outcomes.
This level of control does not apply to every AI use case
This level of control does not apply to every AI use case. If a staff member uses an approved AI tool to rewrite a public blog paragraph, summarise a public report or brainstorm a meeting agenda with no personal or confidential data, the risk is low. You still need a usage policy, but you do not need a full security review for every harmless prompt.
It also does not apply in the same way to fully offline tools running on local hardware with no external connectivity, no personal data and no business integration. That can reduce supplier and transfer risk, although it creates other duties around device security, updates, model quality and access control.
Do not over-engineer the first step. Many SMEs should start with approved tools, staff training and clear red lines before building custom AI systems. The businesses that get into trouble are usually not the ones asking too many security questions. They are the ones connecting tools to live data before anyone has decided what should happen when the tool gets it wrong.
Use this checklist before connecting AI to business data
Use this checklist before connecting AI to business data. First, write down the business purpose. If you cannot explain the workflow in one paragraph, it is too vague. Second, list the data sources. Include hidden sources such as attachments, archived folders, private channels, CRM notes and call transcripts.
Third, classify the data. Identify personal data, confidential data, restricted data and anything that should never be processed by AI. Fourth, map the supplier chain. Name the application vendor, model provider, cloud provider, subprocessors and support access. Fifth, check the contract. Look for training use, retention, deletion, audit logs, breach notice, data location, subprocessors and termination help.
Sixth, reduce permissions. Give read-only access before write access. Give one folder before the whole drive. Give one team before the whole tenant. Seventh, test with hostile prompts and awkward documents. Include prompt injection attempts, sensitive files, wrong user roles and requests for information the AI should refuse.
If you want a practical review of whether your proposed AI workflow is safe enough to connect to business data, book a free call. We will tell you plainly whether the risk is manageable, whether the scope needs tightening, or whether the data should stay out of AI for now.
Most AI risk conversations are too vague
Most AI risk conversations are too vague. They focus on scary model behaviour, science fiction or whether a tool is generally secure. The practical business risk starts when AI is connected to your actual data.
If an AI tool can read customer records, sales notes, board papers, HR documents, contracts, email threads or finance exports, it becomes part of your information security environment. If it can also update records, send messages, create tasks or trigger workflows, it becomes part of your operational control environment too.
That is a different category of decision from letting staff use a public chatbot to draft generic copy. A connected AI assistant may be able to retrieve personal data, infer commercially sensitive patterns, summarise confidential documents, expose information to the wrong user, or take an action based on a malicious instruction hidden inside an email or document.
The UK context matters. GOV.UK states that data protection in the UK is governed by the UK GDPR and the Data Protection Act 2018, and that personal information must be used fairly, lawfully and transparently, limited to what is necessary, kept accurate, and handled securely. Those duties do not disappear because the processing is done through AI. Source: GOV.UK data protection guidance.
The honest answer is that AI can be connected safely, but only if you know exactly which data it can see, why it needs that data, what the supplier does with it, how access is restricted, how outputs are checked, and how incidents are logged.
The first security risk is data leakage
The first security risk is data leakage. Staff may paste confidential material into unauthorised tools, or an approved AI system may send prompts, files or logs to a supplier environment that has not been reviewed. Samsung became the named example in 2023 when employees reportedly entered semiconductor source code and internal meeting content into ChatGPT. Source: Tom's Hardware reporting on Samsung.
The second risk is over-permissioned AI. Many AI pilots start with broad access because it makes the demo work. That is dangerous. An assistant that only needs to answer questions about a product manual should not have access to payroll folders, private inboxes or exported customer lists. Least privilege still applies.
The third risk is prompt injection. This is where malicious instructions are placed inside data the AI reads, such as a web page, email, PDF, support ticket or document. The AI may treat that hostile text as an instruction. The NCSC warns that AI systems need controls around data access, generated content sensitivity, external API use, action restrictions and least privilege. Source: NCSC secure AI design guidance.
The fourth risk is identity confusion. If every AI action happens through a shared admin account, you cannot tell who asked the system to retrieve a file, change a record or send an output. For connected AI, you need named users, agent identities, approval records and audit logs.
The fifth risk is supplier and subprocessor exposure. Your data may pass through model providers, hosting providers, observability tools, vector databases, transcription services and integration platforms. You need to know who they are, where data is processed, how long logs are retained, whether prompts are used for training, and how deletion works.
| Risk | What it looks like | Basic control |
|---|---|---|
| Data leakage | Staff paste sensitive files into unapproved AI tools | Approved tools, blocked consumer apps, staff guidance |
| Over-permissioning | AI can access far more data than the workflow needs | Read-only access, least privilege, data scopes |
| Prompt injection | Hidden instructions in emails or documents manipulate the AI | Tool restrictions, approvals, output validation |
| Weak audit trail | No clear record of who asked the AI to do what | User-level logs, agent identities, retention policy |
| Supplier risk | Unknown processors, unclear retention, poor deletion rights | DPA review, subprocessor list, exit plan |
The privacy risk is not simply that personal data might leak
The privacy risk is not simply that personal data might leak. It is that the business may process personal data in a way that is unnecessary, unexpected, poorly explained or impossible to justify.
Under UK GDPR, you need a lawful basis for processing personal data. If you rely on legitimate interests for an AI workflow, the ICO says you need to identify the legitimate interest, show the processing is necessary, and balance it against the individual's interests, rights and freedoms. Source: ICO guidance on lawfulness in AI.
For many UK SMEs, the weak point is necessity. It is easy to say, "AI needs access to everything so it can be helpful." That is not a serious data protection argument. If the workflow is invoice coding, the AI probably does not need full CRM notes. If the workflow is customer service triage, it probably does not need HR files. If the workflow is sales email drafting, it probably does not need raw finance exports.
Privacy risks also include purpose creep. A tool approved for internal document search starts being used for staff performance review. Sales call transcripts collected for training start being used for automated scoring. Customer support tickets used to improve response speed start being mined for marketing segmentation. Each change may alter the lawful basis, transparency duties, retention period and risk profile.
Then there is accuracy. AI can summarise confidently and still be wrong. If inaccurate AI output is used in decisions about customers, employees, credit, complaints, recruitment or service eligibility, the privacy issue becomes more serious. The duty to keep personal data accurate still applies.
The risk is not theoretical
The risk is not theoretical. The Department for Science, Innovation and Technology and the Home Office reported in the Cyber Security Breaches Survey 2025/2026 that 43% of UK businesses experienced a cyber security breach or attack in the previous 12 months. That equates to approximately 612,000 UK businesses. Medium businesses reported 65% and large businesses 69%. Source: Cyber Security Breaches Survey 2025/2026.
AI changes the blast radius. A normal phishing email might trick one person. An AI assistant connected to email, CRM and documents may retrieve more context, summarise it, expose it or act on it. That does not mean every connected AI system is unsafe. It means the old assumption that a document is passive no longer holds. If an AI can read it and use tools, a document can influence behaviour.
For a UK SME, the most likely incidents are not cinematic hacks. They are ordinary operational failures: someone connects an AI note-taker without checking consent and retention, a department uploads a customer list into a public tool, an assistant indexes all SharePoint folders instead of one approved library, or a supplier's AI feature is enabled without a data protection review.
The cost is not only regulatory. It can include incident response, legal advice, customer notification, lost contracts, cyber insurance problems, staff time, supplier remediation and reputational damage. A modest AI pilot can become expensive if nobody knows what data moved where.
Start with a data map
Start with a data map. List the systems, data types, users, suppliers and actions involved in the workflow. Do not approve "AI connected to the business" as a concept. Approve a specific workflow with a specific boundary.
Use read-only access first. If the AI does not need to write, delete, export, email or update records, do not give it that permission. If it eventually needs action rights, add approval gates for high-risk actions such as sending external emails, changing customer records, exporting reports, deleting files or making decisions that affect people.
Separate instructions from untrusted content as far as the architecture allows, but do not pretend this removes prompt injection risk. Treat model output as untrusted until checked by deterministic rules, permission checks or human approval. The more power the AI has, the less you should rely on the model's own promise to behave.
Check the supplier contract. You need clear answers on data processing roles, UK GDPR processor terms, subprocessors, international transfers, retention periods, prompt logging, training use, deletion, security certifications, breach notification and exit support. If the vendor cannot answer, do not connect sensitive data.
Run a Legitimate Interests Assessment or Data Protection Impact Assessment where appropriate. The ICO explains that a DPIA helps organisations systematically analyse, identify and minimise data protection risks, and that it should be reviewed if the processing changes. Source: ICO DPIA guidance.
Finally, log enough to investigate. The NCSC's secure operation guidance says organisations should monitor and log inputs such as inference requests, queries or prompts in line with privacy and data protection requirements, to support audit, investigation and remediation. Source: NCSC secure operation guidance.
- Define the workflow and business owner.
- Classify the data before connecting it.
- Use read-only and least privilege by default.
- Block unapproved consumer AI tools for sensitive work.
- Review supplier terms, subprocessors and retention.
- Use human approval for high-risk actions.
- Keep logs that show user, prompt, data source, tool action and output.
- Test with hostile documents, bad prompts and unusual user requests before launch.
This level of governance may be excessive for very low-risk uses
This level of governance may be excessive for very low-risk uses. If you are using AI to rewrite public marketing copy, brainstorm blog titles, generate generic meeting agendas or summarise information that is already public, the security and privacy burden is much lower.
It also may not apply if the AI tool is completely isolated from personal data, confidential business information and operational systems. For example, a local model used to classify non-sensitive product descriptions may need normal IT controls, but it may not need a full DPIA.
However, be careful with the phrase "non-sensitive". Internal documents often contain names, emails, customer references, pricing, supplier information, employee comments or commercially useful detail. A folder can look harmless until it is indexed and searchable across the whole business.
This guidance also does not mean every AI project needs enterprise-level bureaucracy. A small business does not need a 60-page policy before trying AI. It does need a clear yes or no list for data types, a named owner, approved tools, sensible access controls and a basic incident plan.
The practical answer is to connect AI gradually
The practical answer is to connect AI gradually. Start with one workflow, one data set and one business owner. Use a controlled pilot with synthetic, redacted or low-risk data first. Move to real data only when you know the access boundary, supplier position, logging model and approval process.
A good first project is usually internal knowledge retrieval from a curated document set, support ticket triage with human review, or sales call summarisation with consent and retention controls. A poor first project is giving an AI agent broad access to email, CRM, finance and document storage with permission to act autonomously.
Budget for governance. For a UK SME, a sensible security and privacy review for a connected AI pilot might be a few days of internal IT, operations and management time, plus external help if the data is sensitive or regulated. If the use case touches health data, children, employment decisions, financial services, legal advice or vulnerable people, the review needs to be stronger.
If a supplier promises "bank-grade security" but cannot tell you whether prompts are retained, where data is processed, who the subprocessors are, whether your data trains models, how access is logged, and how deletion works, that is not enough.
If you want to explore whether connecting AI to your business data makes sense, start with a risk review of one workflow. No pitch, no pressure. The useful question is not "Can AI access our data?" It is "Which data should AI access, for which purpose, under which controls?"
When businesses talk about AI risk
When businesses talk about AI risk, they often focus on the model itself. In reality, the bigger issue is what the model can reach. A general-purpose chatbot with no business access is limited. An AI assistant connected to your email, CRM, shared drive, contracts, and customer records becomes far more useful, but also far more sensitive.
The biggest risks are usually ordinary operational failures. Someone connects the wrong folder. A tool is granted read access to everything when it only needed one project space. An employee pastes customer data into a consumer tool outside approved controls. An AI note-taker records a confidential meeting without clear consent or retention rules. None of this requires a dramatic cyberattack. It just requires weak governance.
That is why connecting AI to business data should be treated like any other privileged system integration. If you would not let a new SaaS product have broad access without a review, you should not do it for an AI tool either.
There are five common failure points
There are five common failure points. First, data leakage. Sensitive data may be exposed through prompts, logs, exports, or weak vendor controls. Second, over-permissioning. Teams often grant broad access because it is faster than designing the minimum required scope. Third, retention confusion. Staff may not know whether prompts, uploaded files, or meeting transcripts are stored, for how long, and under what terms. Fourth, weak accountability. If outputs are wrong or a privacy incident occurs, nobody is sure who owns the failure. Fifth, policy drift. A tool that was acceptable six months ago may have changed its terms, training defaults, or feature set.
For UK firms, these risks also intersect with contractual confidentiality, sector rules, and data protection obligations. If personal data is involved, UK GDPR still applies. If regulated data is involved, your regulator will not accept AI novelty as an excuse.
The answer is not to ban every connection
The answer is not to ban every connection. It is to control them properly. Start with data classification. Which data can be used with public models, which requires enterprise-managed tools, and which should never leave controlled infrastructure? Then apply least-privilege access. Give AI systems only the data and tool access they need for the workflow in question.
Next, review vendors properly. Look at retention policies, auditability, access controls, regional hosting options, and contractual terms. If a supplier cannot explain what happens to your data, that is already your answer. Then add logging and oversight. You need to know what was accessed, by whom, for what purpose, and with what result.
Finally, train your staff. Many privacy failures come from normal employees trying to be helpful and fast. Clear guidance on approved tools, permitted data, and verification rules prevents far more risk than vague warnings ever will.
Sometimes the honest answer is not yet
Sometimes the honest answer is not yet. If your data is badly organised, permissions are chaotic, and nobody owns information governance, connecting AI can magnify those existing weaknesses. AI does not clean up messy foundations by itself.
It may also be the wrong time if your use case is still vague. Businesses often rush to connect AI to multiple systems before they have defined the outcome they want. Start with one narrow workflow, one approved tool, and one clear success measure. Then expand once the controls are proven.
If you cannot explain why the AI needs access, what data it should see, and how a human will check the result, you are not ready for the connection yet.
If you want to explore this properly, start with a workflow and data review. That usually reveals the real risks much faster than a generic policy workshop.
Who this approach suits
This applies if you are planning to connect AI to live business data: CRM records, email, SharePoint, Google Drive, finance tools, support tickets, HR files, contracts, call transcripts or internal knowledge bases. It is especially relevant if the AI can search across systems, write back to them, trigger workflows or answer staff questions using sensitive company information.
It does not mean you should avoid AI. It means you should start with narrow use cases, read-only access, clear ownership, supplier review, logging and a written data protection assessment before giving an AI tool broad access. If your business cannot currently explain who can access what data, AI will not fix that. It will usually make the access problem faster and harder to see.
Who this approach suits
This article is right for you if you are considering connecting AI to internal documents, inboxes, CRM records, finance systems, customer support tools, or file storage and want the honest view on risk before you proceed.
It is less useful if you are only looking for a simplistic yes-or-no answer. The real question is not whether AI access is safe in the abstract. It is whether your architecture, permissions, and governance make it safe enough for your specific data.
Related buying guidance
For the related buying decision, read What risks do we take if we cannot account for the AI tools our business uses?.
For the related buying decision, read Can AI help me understand my business data if it is spread across different tools?.
Browse the problems guidance pillar for more buyer questions.
Is This Right for You?
This guidance applies if your AI tool can access CRM records, inboxes, documents, finance data, HR files, customer support tickets, call transcripts, sales notes, personal data or confidential business information. If the tool can retrieve, summarise, classify, write, send, update or trigger actions, you need a proper risk assessment before connecting it.
It is less relevant if your team is only using a public AI tool for low-risk drafting with no personal data, no client information and no confidential material. Even then, you still need a staff policy, because accidental copy and paste is one of the simplest ways sensitive data leaves the business.
The honest test is this: if you would not email the data to an unknown supplier, do not paste it into an unmanaged AI tool. If you would not give a junior employee unrestricted access to the system, do not give that access to an AI assistant without logging, limits and review.